Strengthening Endpoint Security with CrowdStrike EDR
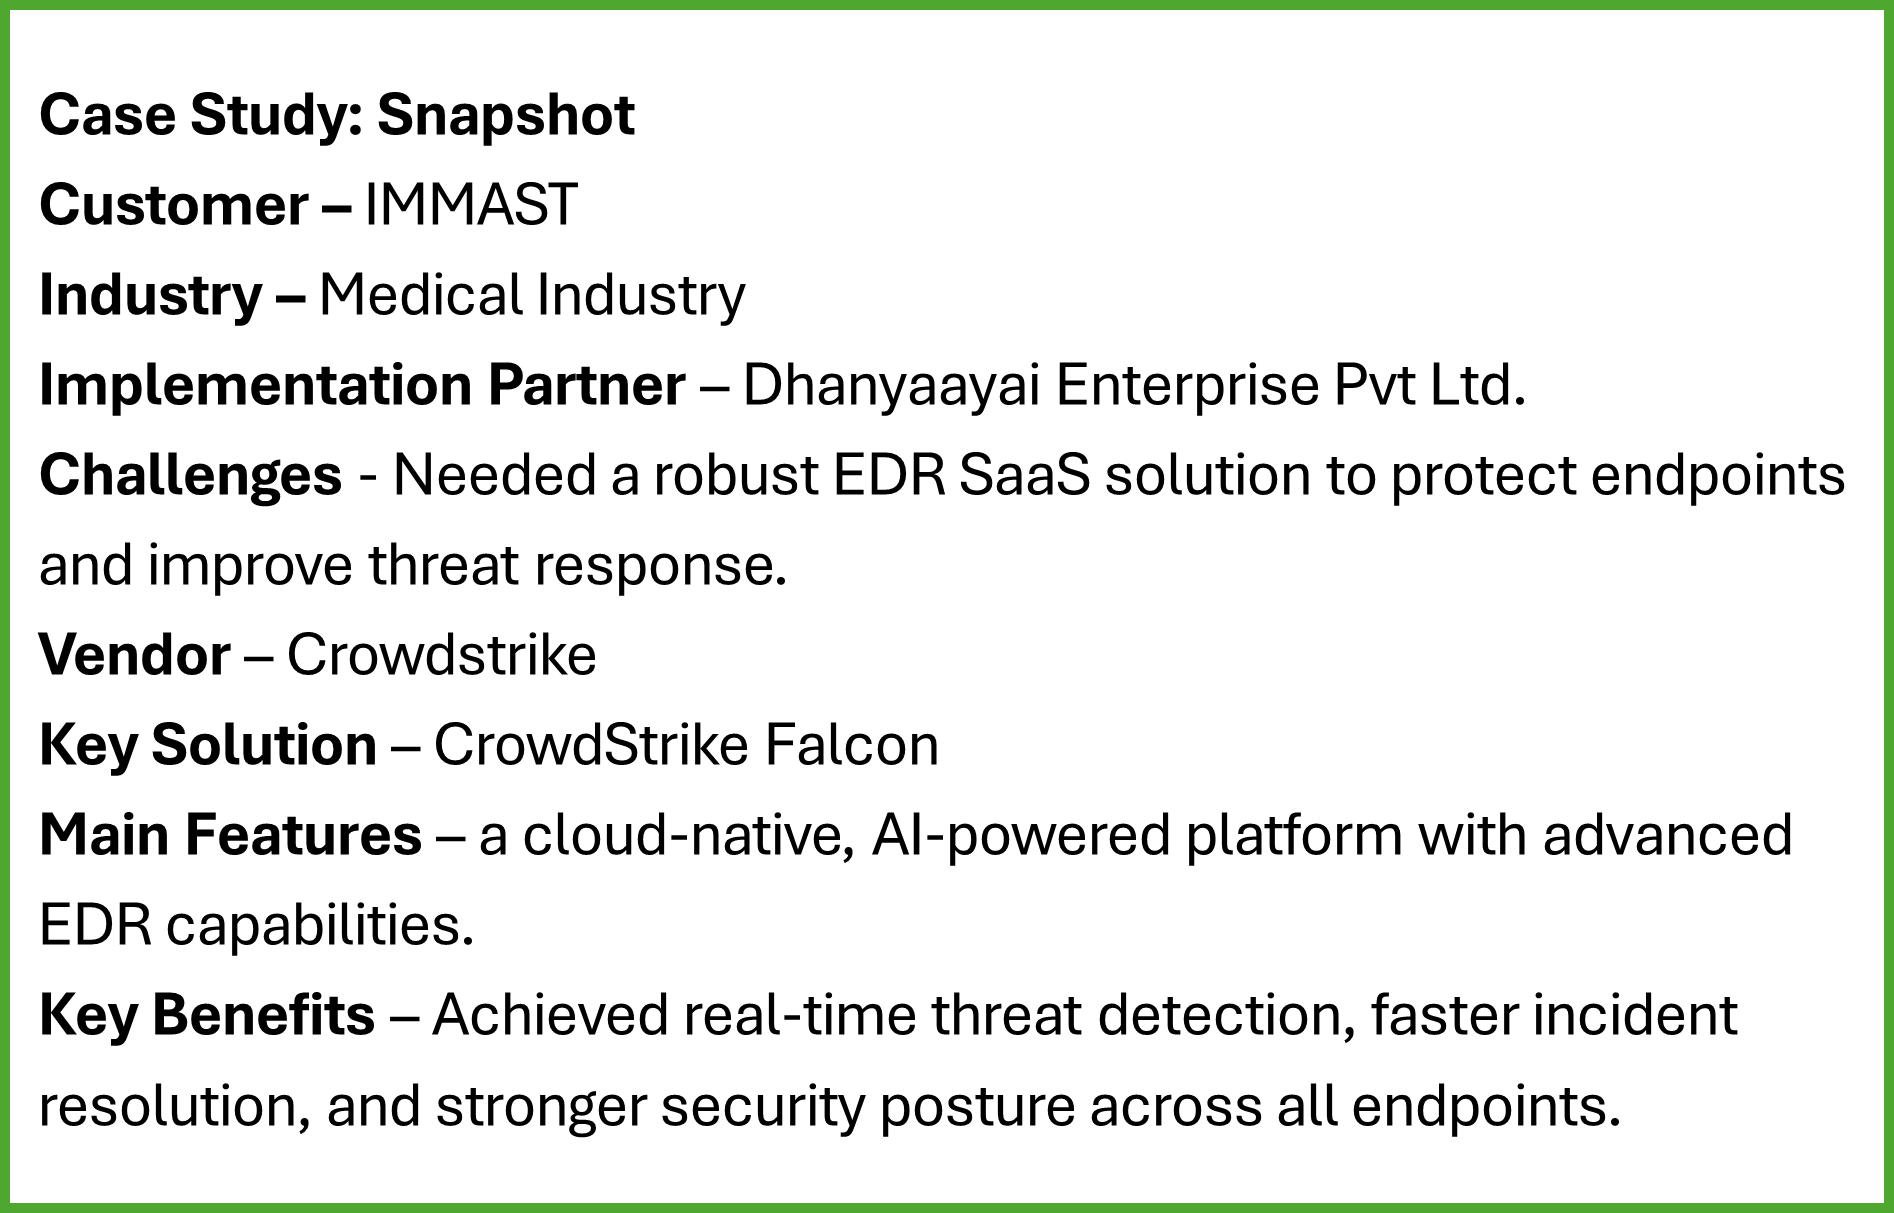
Customer Requirement:
A leading enterprise approached us seeking the best EDR
(Endpoint Detection and Response) SaaS solution to secure its growing
number of endpoints.
With the rise of sophisticated cyber threats, their existing security setup
struggled to provide real-time visibility, rapid incident detection,
and effective response capabilities. The customer wanted a cloud-based,
scalable, and AI-driven solution to safeguard their workforce, no matter
where they were located.
Our Solution:
After a detailed assessment of the customers’
infrastructure, security needs, and operational challenges, we recommended CrowdStrike
Falcon, a modern, cloud-native security platform renowned for its
robust EDR capabilities.
Key highlights of our proposed solution:
- Advanced
Endpoint Protection – Leveraging signature-less, AI-powered threat
detection to stop known and unknown attacks.
- Real-time
Threat Intelligence – Enabling proactive defense with constantly
updated global threat insights.
- Cloud-Native
Architecture – No heavy on-premises infrastructure, ensuring quick
deployment and seamless scalability.
- Enhanced
Incident Response – Integrated tools for faster detection,
investigation, and remediation of security incidents.
By adopting CrowdStrike Falcon, the customer was able
to strengthen their overall security posture while benefiting from continuous
protection and monitoring.
Implementation & Outcome:
The implementation was carried out smoothly with minimal
disruption to business operations. Once live, the customer’s security team was
able to:
- Identify
and respond to threats in real time using Falcon’s intuitive
dashboards and alerting mechanisms.
- Leverage
advanced EDR capabilities to investigate suspicious activity in depth,
reducing false positives and improving accuracy.
- Accelerate
incident resolution by automating parts of the investigation and
response workflow.
- Enhance
operational efficiency by consolidating threat intelligence,
detection, and response into a single platform.
Within weeks, the customer saw a significant improvement
in threat visibility and response speed, enabling them to mitigate risks
before they could impact critical systems or data.
With CrowdStrike’s AI-driven, cloud-native EDR in place,
the customer now operates with confidence, knowing that their endpoints are
protected against the most sophisticated and evolving cyber threats — anytime,
anywhere.